Test critical infrastructure the way an attacker would, without taking it down.
The systems that run a physical process cannot be rebooted to see what happens. Radius observes them passively first, attacks only what you authorize, asset by asset, stops before impact, and proves which paths reach a controller. Once you fix a path, it attacks that path again.
What matters in critical infrastructure
Three things decide whether a run on a plant is worth doing: what each path reaches, whether the evidence stands up to someone who was not in the room, and whether the fix held.
What the path reaches
Radius orders every path by the asset at the end of it. A foothold on a workstation that can reach a controller outranks a critical CVE on a printer, because the controller is what an attacker is after.
Evidence someone else can check
Operators under supervision are asked to prove control. Every finding carries the command, the timestamp and how far the chain got, and every run ends in a compliance report: what was tested, when, under whose authorization, with what outcome.
A fix that held
A fix is closed when Radius attacks the same path again and fails. The re-attack is dated and in the report, and the record carries to the next run, so the next decision starts from what was found before instead of from zero.
Protect
Safety controls built for hardware you cannot reboot
On an industrial network the safety controls are the product. They live in the engine and are checked before every action, and they are the reason a run can touch a production network at all.
Passive first
Discovery starts with what can be observed without sending a packet to a controller. Active probing is switched on per asset, in the rules of engagement, and never by the engine on its own.
Rules per asset, enforced by the engine
The rules you sign are loaded into the engine and checked before every action. Non-bypassable safety patterns sit above your blocklist and the per-asset rules.
The attack stops before impact
Radius runs the real chain to the point that proves the path, such as a foothold on the engineering workstation or a session on the historian, and stops there. The step that would affect the process is not part of the run.
A stop button that works mid-run
The run halts, the trail records where and why, and it resumes only when you say so.
Test
The real chain, from the corporate network to the controller
Most paths into a plant start outside it: a remote-access appliance, an identity that both sides trust, a historian with a second interface. Radius reasons over IT, cloud and the plant in one graph, so the chain is followed across the boundary instead of stopping at it.
Across the boundary
The chain runs from the corporate side into the plant, through the appliance, the identity bridge and the engineering workstation, to the point that proves it can reach the controller.
Proof, hop by hop
Each hop is recorded with the command, the timestamp and what came back. Each decision the interceptor took sits in the safety trail next to it, so an operations manager can read what was done to the plant, action by action.
Attacked again after the fix
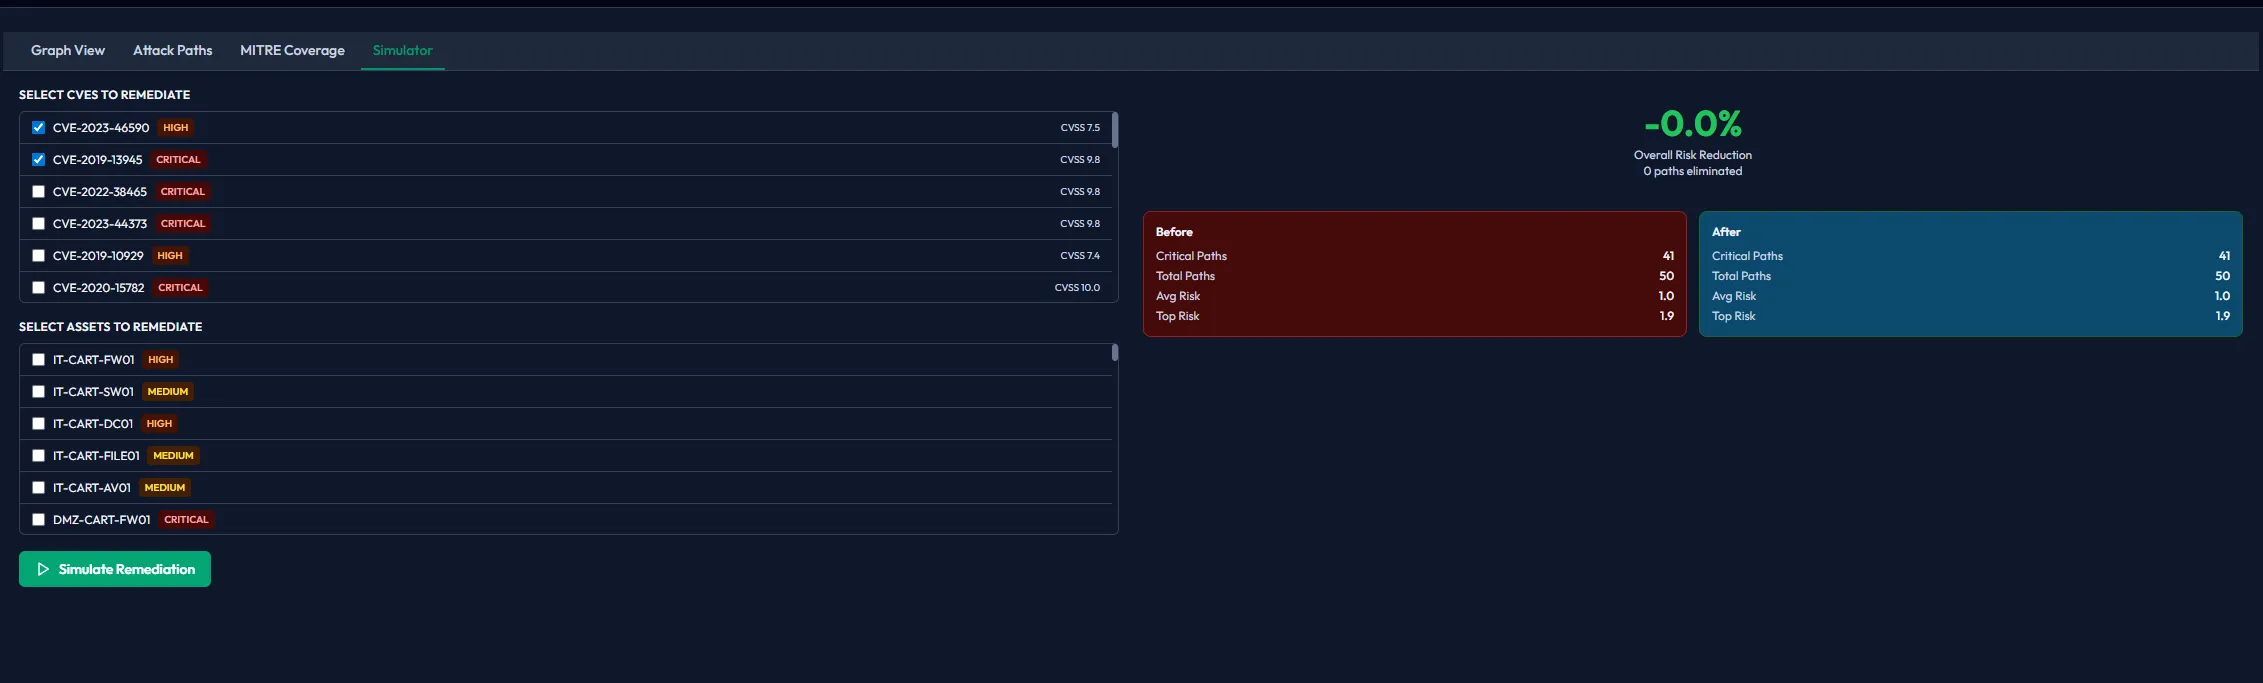
Once the chokepoint fix lands, such as a revoked trust or a segmented workstation, Radius attacks the same path again. The ticket closes only when the re-attack fails.
What a run delivers
Three reports (executive, technical, compliance), each at run, asset and finding level, plus the safety trail for every action. A run takes 2 to 4 weeks at a fixed price agreed before it starts, and the run is credited if you continue to continuous coverage.
Beyond the plant
The same engine covers IT, cloud and identity
Critical infrastructure is where the safety controls matter most, and the same run covers the corporate network, the cloud tenants and the identities that lead into it. Findings go to the tools your teams already work in, with the validated chain behind each one: Jira, ServiceNow, Splunk, Microsoft Sentinel, AWS Security Hub, and signed webhooks for the rest.
Questions we get about critical infrastructure
Is Radius safe for a production plant?
Which protocols and device types are in scope?
What if we have to stop mid-run?
Does Piscium certify compliance?
How often should a run happen?
Related Resources
Scope a run against the plant.
A 30-minute call, a draft of the rules of engagement per asset, and a fixed price. The run starts when you sign, and not before.